Cloud Isolation Broken: How Wiz Uncovered a Major Microsoft Cloud Vulnerability Before Hackers Could Strike
Cybersecurity firm Wiz discloses a major Microsoft cloud isolation flaw that could have exposed thousands of enterprise clients. Read the full analysis.
In this article
In the modern enterprise landscape, cloud computing is the digital bedrock of global commerce, hosting sensitive corporate assets, proprietary databases, and private communication channels. But what happens when the digital walls separating these enterprise environments crumble?
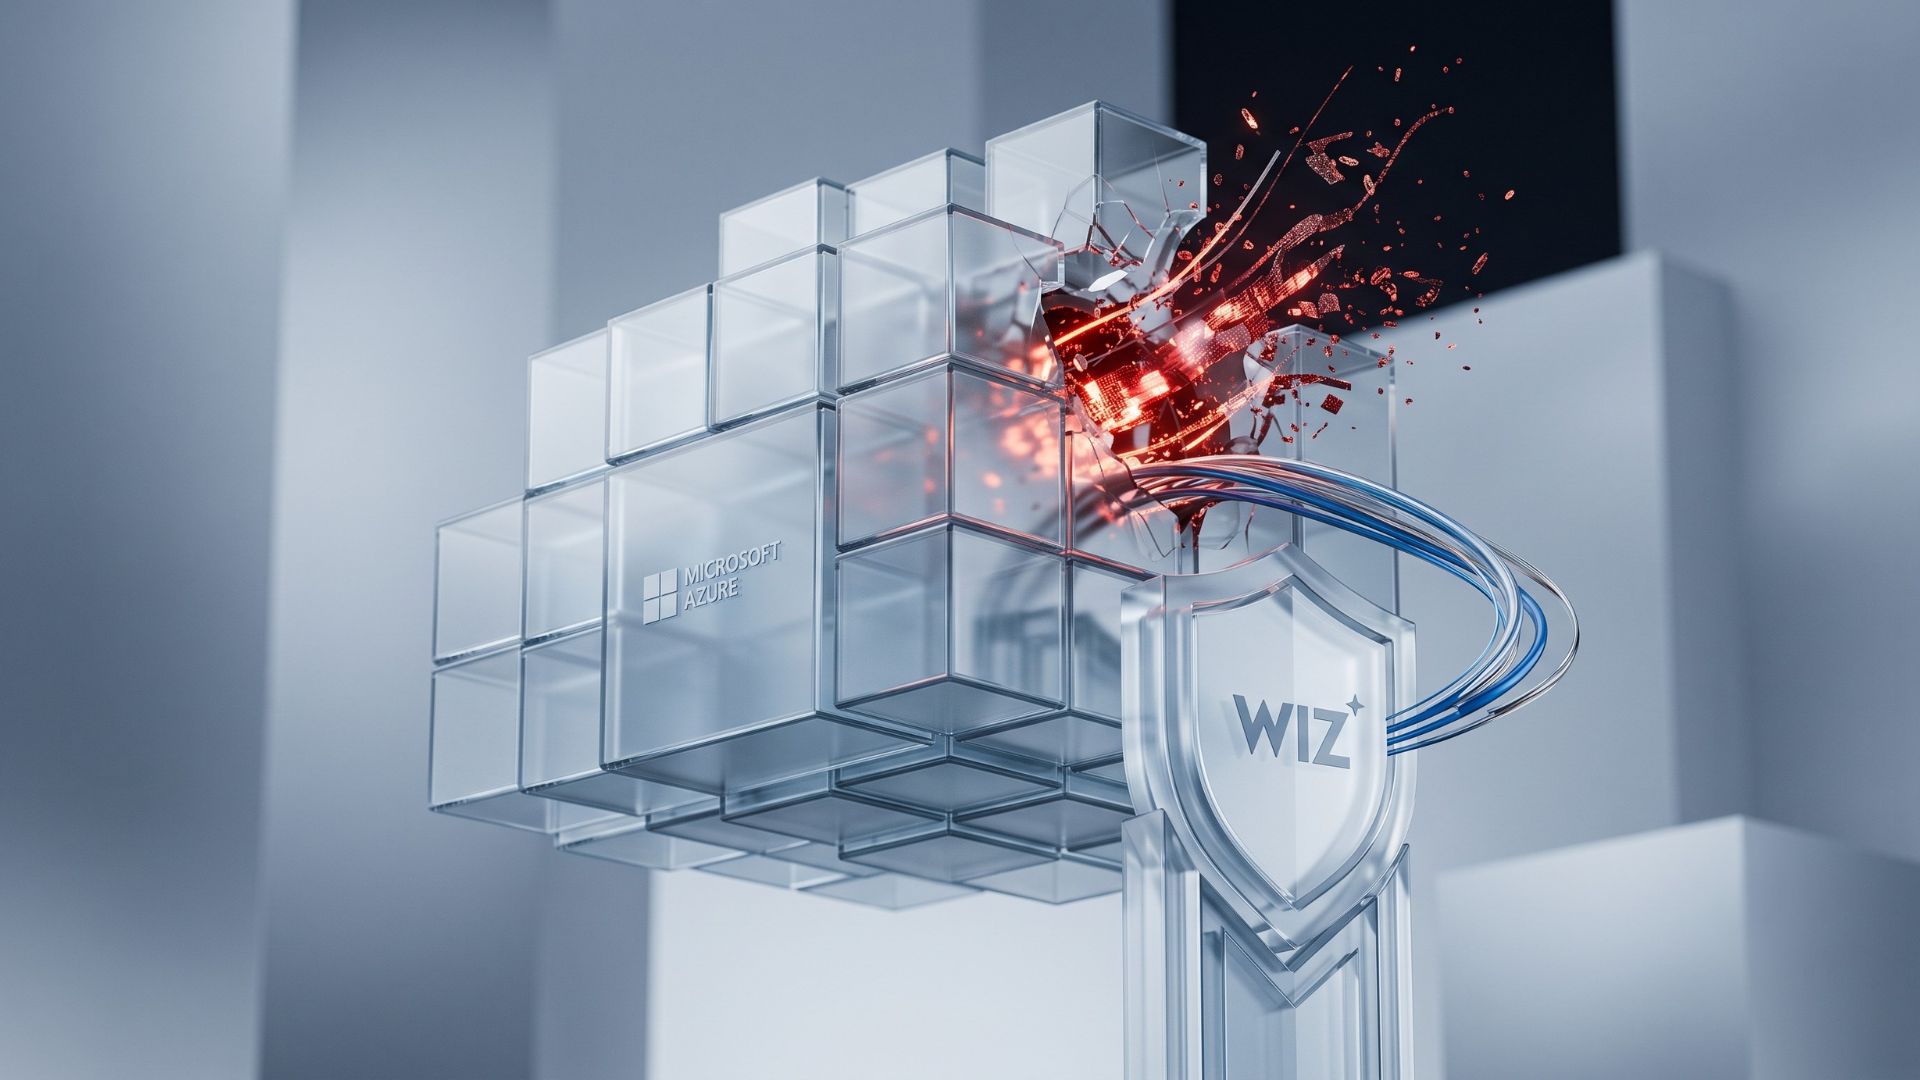
In a disclosure today, prominent cybersecurity firm Wiz revealed a critical vulnerability in Microsoft’s cloud environment that could have led to a mass exposure affecting thousands of enterprise clients. The finding highlights a recurring, systemic vulnerability in centralized cloud platforms: tenant isolation failures.
Inside the Flaw: What Wiz Discovered
In cloud architecture, multi-tenancy allows multiple organizations to share physical server infrastructure while relying on logical boundaries (isolation) to keep each customer’s data private and secure.
According to Wiz researchers, the newly identified vulnerability compromised these critical isolation safeguards. Had malicious actors discovered and exploited the flaw before it was remediated, they could have bypassed security boundaries, gaining unauthorized access to cross-tenant data, internal configurations, and sensitive customer assets hosted on Microsoft’s cloud infrastructure.
The flaw did not just threaten isolated accounts; it held the potential for sweeping, widespread exposure across Microsoft’s vast client ecosystem, a major threat to global enterprises, financial institutions, and tech platforms reliant on Microsoft’s cloud architecture.
A Narrow Escape: Mitigation and Response
Fortunately, Wiz responsibly disclosed the vulnerability under coordinated disclosure guidelines, alerting Microsoft to the weakness before any known public exploit occurred.
Upon notification, Microsoft moved swiftly to patch the flaw on the backend, mitigating the risk across its infrastructure. Because the fix was deployed globally at the architecture level, corporate users and cloud administrators generally did not need to take manual action to patch their environments.
However, the discovery serves as a dramatic reminder of the high-stakes game played in cloud security: a single foundational flaw can compromise millions of connected businesses simultaneously.
The Enterprise Dilemma: Rethinking Centralized Risk
For enterprise leaders and blockchain developers alike, this incident underscores the double-edged sword of centralized cloud services:
- The Single Point of Failure: While hyperscale cloud providers offer unparalleled scale and convenience, they inherently centralize risk. A single backend bug can jeopardize thousands of independent companies simultaneously.
- The “Black Box” Problem: Enterprise customers rarely have visibility into backend cloud operations, making them entirely dependent on third-party audits and security researchers like Wiz to uncover platform-level vulnerabilities.
- The Web3 & Decentralized Push: As major security flaws continue to surface in traditional cloud architectures, the argument for hybrid, zero-knowledge, and decentralized computing infrastructures (DePIN) continues to gain momentum within the tech ecosystem.
Key Takeaways for Enterprise Leaders and Web3 Teams
- Audit Cloud Configurations: Even when cloud providers manage backend security, organizations must continually audit their identity and access management (IAM) permissions to limit blast radii.
- Implement Defense-in-Depth: Relying solely on platform-level security is no longer enough. End-to-end data encryption and strict zero-trust access controls ensure that even if cloud isolation is breached, underlying data remains unreadable.
- Diversify Critical Infrastructure: High-stakes applications should consider multi-cloud or decentralized backup strategies to avoid catastrophic operational downtime or systemic data leaks.
As cloud providers continue to scale and integrate increasingly complex AI workloads and cloud-native services, the attack surface expands exponentially. Wiz’s discovery is a victory for proactive cybersecurity, but it also serves as a stark warning: in a hyper-connected, centralized cloud world, trust must be earned and continually verified.
The Morning Brief
Start every day knowing what matters in tech
Six stories chosen by our editors, in your inbox at 06:00 UTC. Free.
Instant notifications in this browser when big news breaks. No email needed, and you can turn them off any time.
See more Blockrora in Google
Make us a preferred source and our stories show up more often in Top Stories.
Founder and Editor at Blockrora. A 20-year veteran of fintech, Web3 ecosystems, and software development, Warren writes on AI infrastructure, decentralised networks, and market reality checks. Trail walker and coffee purist.
More from Warren →