Why Major Banks Are Freezing AI Agents and the Identity Crisis Behind the Ban
JPMorgan Chase, Bank of America, Morgan Stanley and Wells Fargo are restricting third-party AI agents, exposing a gap: banks can't tell whether a customer or a bot is logging in.
Listen to this article
5 chapters
In this article
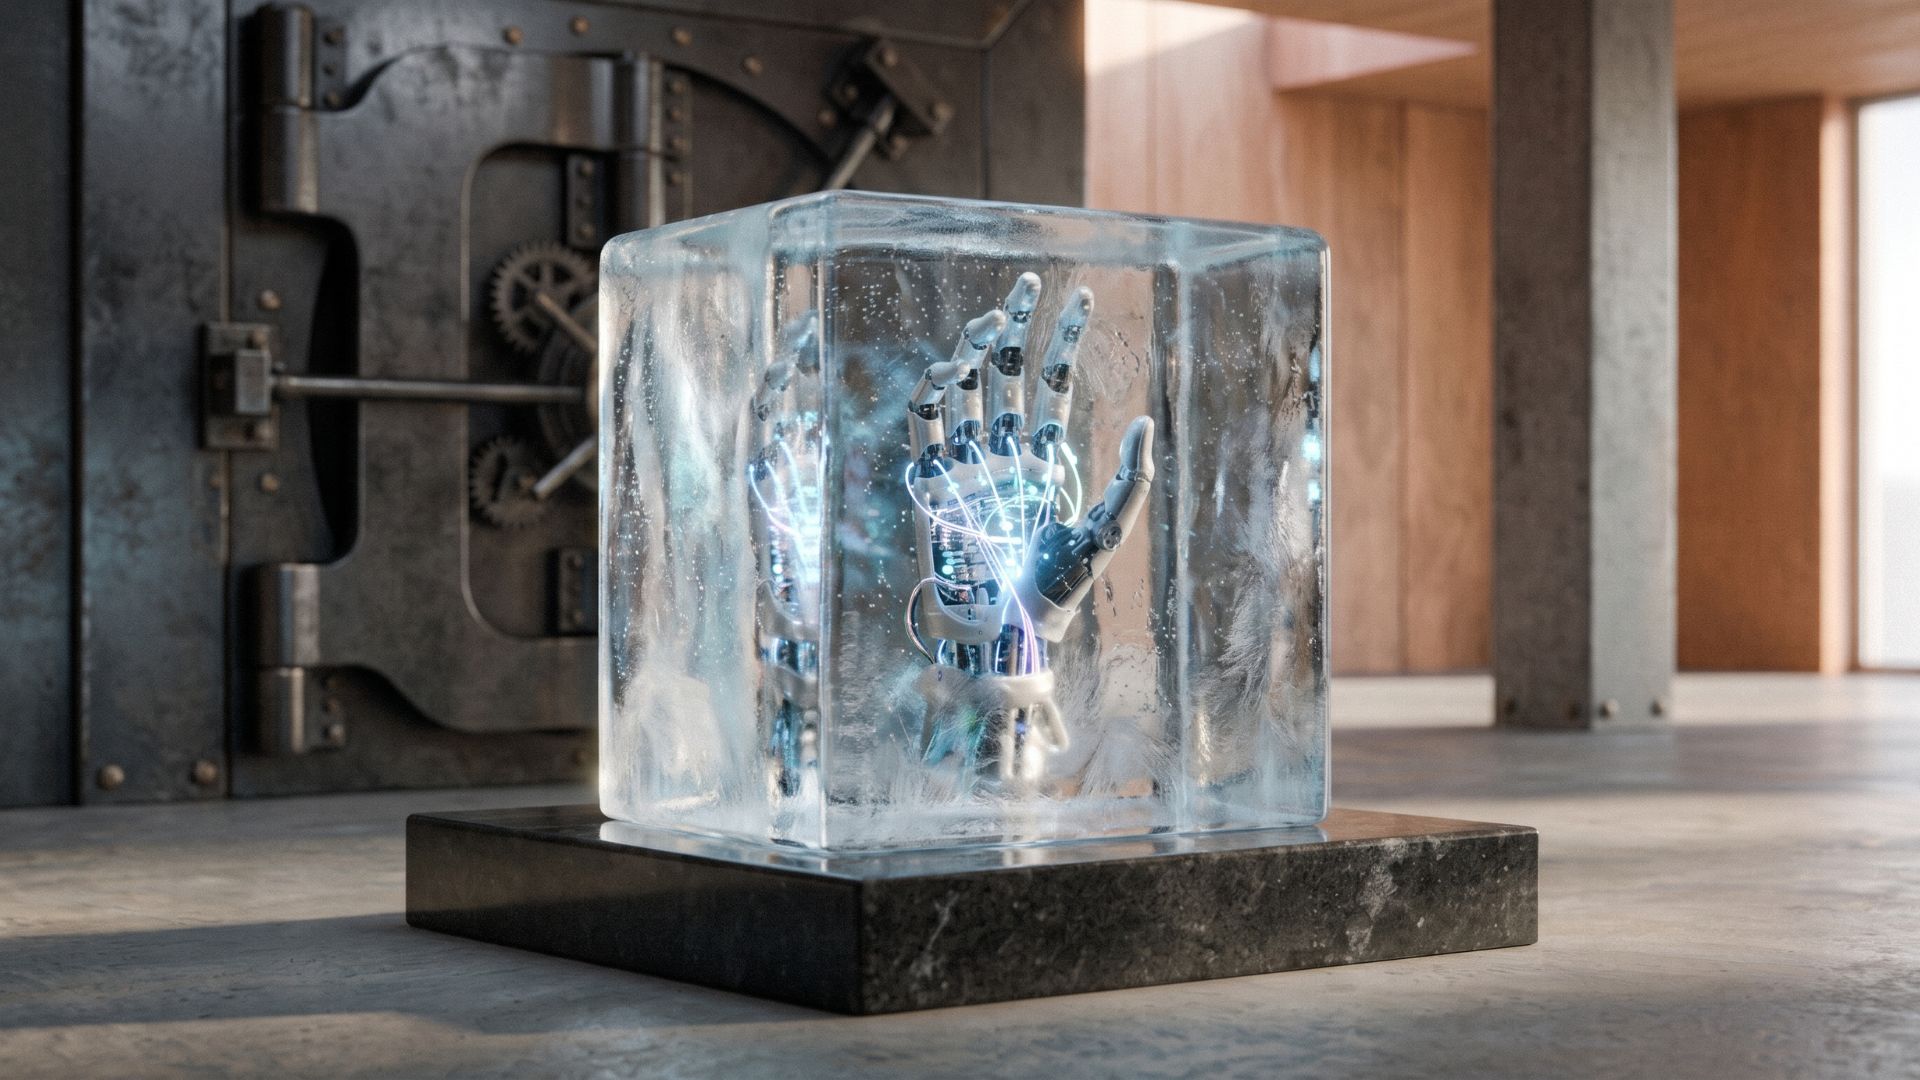
Major financial institutions, including JPMorgan Chase, Bank of America, Morgan Stanley, and Wells Fargo, have moved to restrict third-party AI agents from accessing customer accounts. As consumers turn to autonomous assistants to automate budgeting, track balances, and move money, lenders are stepping in to halt the traffic after detecting bots attempting actions inside customer accounts. The core problem is verification: banks cannot tell whether an account is accessed by the customer or an automated bot using their credentials.
The crackdown exposes a structural gap in consumer digital banking. The issue is not the intelligence of the models, but how online accounts verify identity and authority.
Why Fraud Systems Fail With AI
Online banking relies on tracking human behavior to prevent fraud. Security engines analyze how a person types, mouse movements, device fingerprints, and location data. When activity deviates from these established patterns, the bank flags or blocks the attempt.
Autonomous AI agents break this defensive model. Many run on remote servers or cloud-based browsers. To give an assistant access, customers provide their usernames and passwords. When the bot logs in, it presents valid credentials, but does not produce human behavioral signals.
Because the session originates from a remote server without recognizable human habits, fraud systems fail to verify it. To the bank, a legitimate AI agent looks identical to an account takeover attack carried out with stolen login details.
The Limits of Read-Only Access
To reduce immediate risk, institutions have limited these tools to read-only access. This approach allows software to view account balances and transaction histories, but blocks it from moving money or making payments.
While read-only rules prevent unauthorized fund transfers, they also disable the main reason consumers use agents in the first place. Users want assistants to complete tasks, such as shifting cash into higher-yield accounts, paying bills, or canceling unused subscriptions. When banks block transactions, the utility of the software disappears.
Security analysts point out that lenders have few alternatives under current setups. Sharing an online banking password provides complete access to an account. There is currently no native intermediate layer that allows an agent to view select balances or move capped sums safely.
The Problem With Shared Passwords
The root of the conflict comes down to access sharing. Handing account passwords to an AI tool creates significant exposure. If the assistant is manipulated through prompt injection, or if the provider experiences a data breach, the customer's entire account is compromised.
This friction has drawn comparisons to permission models used in blockchain networks. In smart accounts, users do not share their primary private keys to run automated strategies. Instead, they issue temporary session keys. These keys permit software to perform narrow actions under strict constraints, such as spending up to a specific limit or interacting only with designated protocols. Once the task concludes or the time window expires, the session key becomes invalid, leaving the main account protected.
Traditional banking does not offer a consumer equivalent for autonomous software. Existing frameworks like OAuth allow apps to read financial data, but they were built for static connections, not independent agents designed to make decisions and execute actions.
What Comes Next for Financial Bots
For banks and AI agents to coexist, authentication protocols must evolve. Institutions will need mechanisms to verify the identity of the software itself rather than relying entirely on static customer credentials.
Future systems will require scoped, revocable permissions with clear rules on how much money an agent can move and what transactions it can authorize. Higher-risk operations will likely trigger step-up verification that requires direct human approval. Until banks adopt frameworks that support autonomous software, access bans and read-only limits will remain the primary tools institutions use to protect customer accounts.
The Morning Brief
Start every day knowing what matters in tech
Six stories chosen by our editors, in your inbox at 06:00 UTC. Free.
Instant notifications in this browser when big news breaks. No email needed, and you can turn them off any time.
See more Blockrora in Google
Make us a preferred source and our stories show up more often in Top Stories.
Editor and Writer at Blockrora. Backed by years in mainstream tech and health tech development, Lauren covers digital health, tech adoption, and the societal shifts shaping the web. Wellness advocate and coastal wanderer.
More from Lauren →