Optimjack: Poisoned Optimizely Code Swaps Wallet Addresses
Attackers poisoned Optimizely-hosted scripts on 178 sites, including Ledger, the BBC and HSBC, to swap crypto wallet addresses and skim card data for about 17 hours.
Listen to this article
6 chapters
In this article
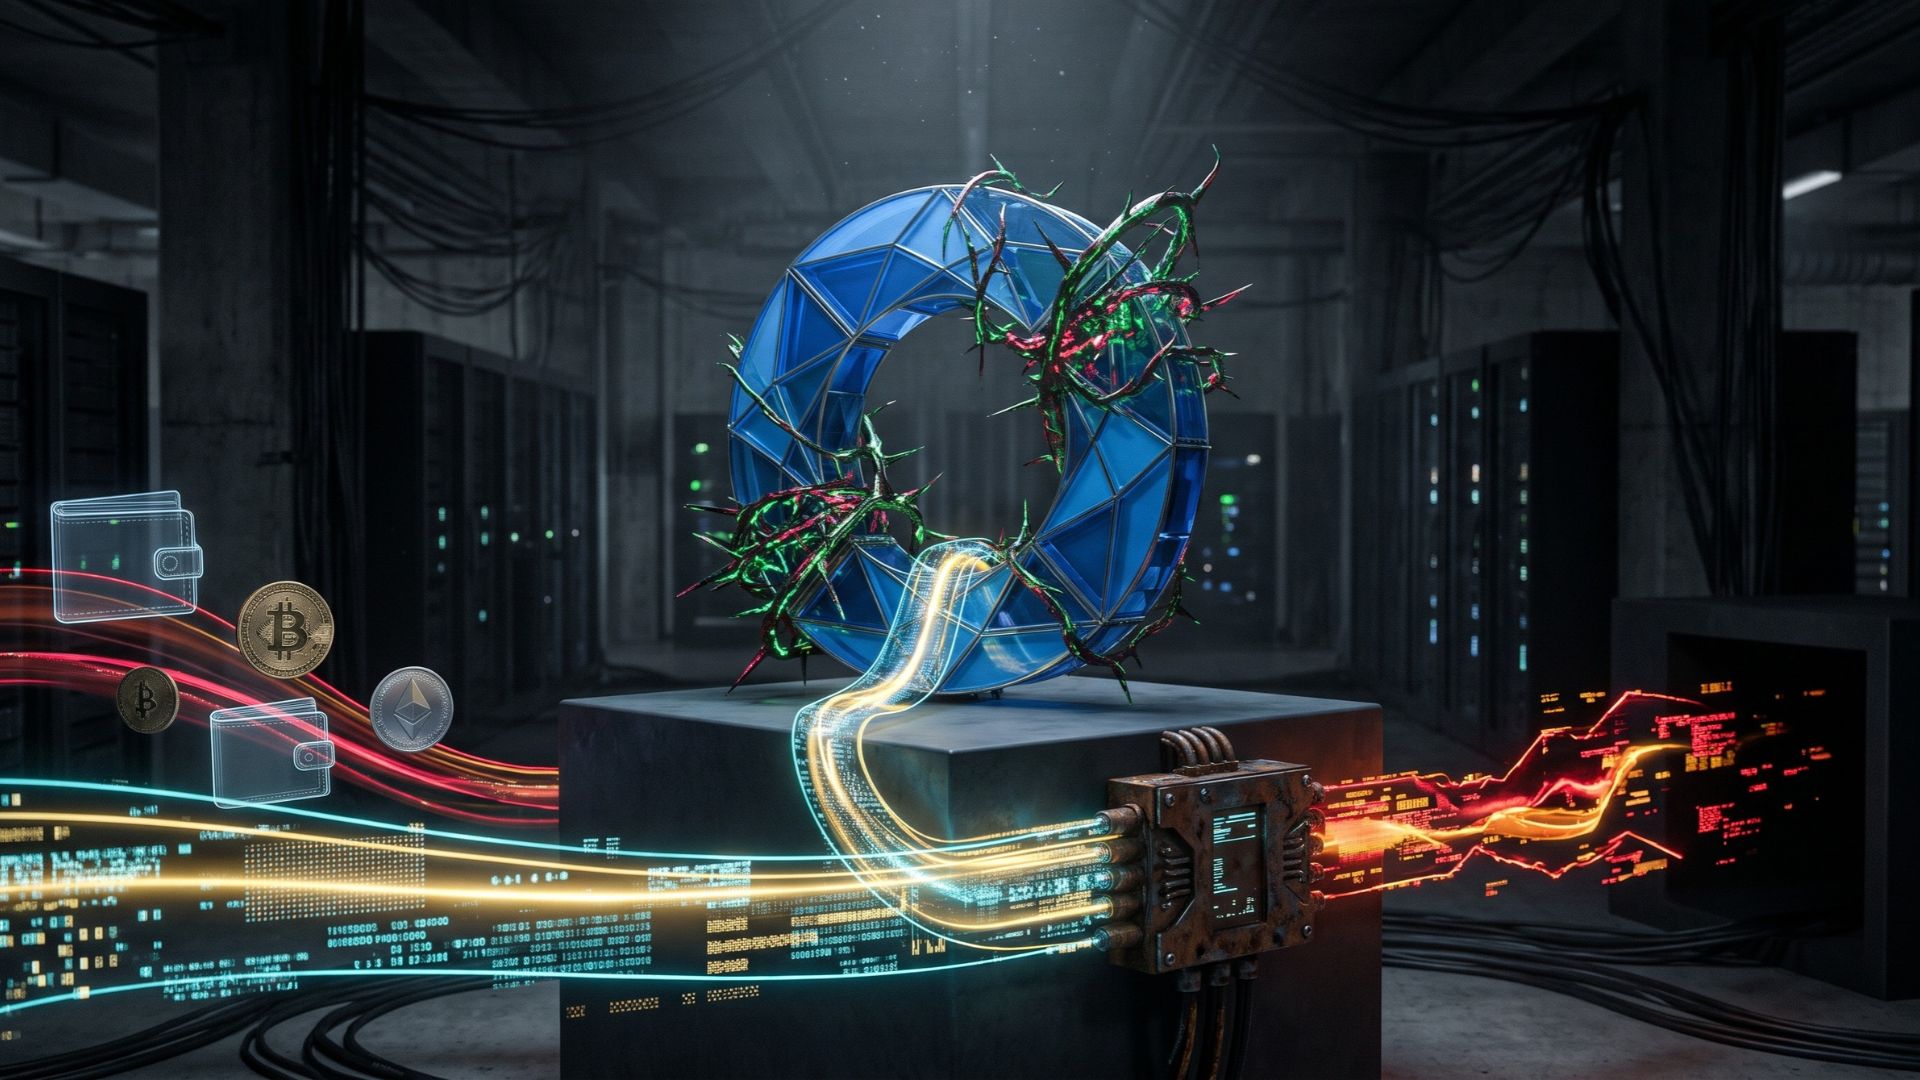
Visitors to 178 well-known websites, from hardware-wallet maker Ledger to the BBC and IKEA, were served code built to hijack crypto transfers and skim card numbers on Monday, 16 November. The attackers never breached those sites directly. Instead, they poisoned scripts delivered through Optimizely, a web experimentation platform the brands use to test and personalise their pages.
The campaign, which researchers have named “Optimjack”, ran for roughly 17 hours before most of the malicious code was pulled.
What researchers found
The alarm came from Scott Helme of Report URI, a firm that sells script-monitoring tools. His team pulled 1,611 Optimizely snippets and found malicious code in 188 of them, belonging to 178 organisations. Helme says the true count is likely higher, since only snippets the team could locate in time were checked.
Banking and finance was the largest group, with 32 organisations including HSBC and Equifax. Six were crypto or trading firms: Ledger, IG, OANDA / Coinpass, interactive investor, TMS Brokers and Betashares. Zoom, Salesforce, GitLab, CNN, Peacock, ASOS and Air France-KLM also made the list, as did Optimizely’s own homepage and login page.
The first injection appeared in the BBC’s snippet at 04:21 UTC. By 21:52 UTC, only one infected snippet remained, belonging to UK broadband provider TalkTalk. All infected files were clean by 23:11 UTC, Report URI later confirmed.
Optimizely acknowledged the incident on its status page early on 17 November. It said an attacker exploited a vulnerability in its Experimentation platform, and that it has fixed the flaw, removed the injected code, secured affected accounts and contacted customers directly.
How the attack worked
Optimizely Web runs on a small JavaScript snippet that each customer loads from Optimizely’s servers. Every snippet has an optional field called Project JavaScript, where customers add custom code that runs on every page. The attacker planted a loader in that field, which fetched a stealer script called track.js from an attacker-owned domain.
Because the snippet still arrived from Optimizely’s own servers, browsers and security allowlists treated it as trusted. Report URI says this was not a cache-poisoning trick: Optimizely’s network delivered exactly what had been written into those projects. Optimizely has since pointed to a flaw in its Experimentation account signup flow. It has not yet explained how that gave the attacker reach into existing customers’ projects.
The payload did four things at once:
Wallet address swapping. It hunted for valid addresses on Bitcoin, Ethereum and EVM chains, TRON, Solana, TON, Litecoin, Bitcoin Cash and Dogecoin, then replaced them with the attacker’s. It hit page text, form fields, links and the clipboard.
Card skimming. Added at 13:43 UTC, this module captured card numbers, expiry dates and CVVs typed into a site’s own forms. Cards entered inside hosted payment frames, such as Stripe or Adyen, were out of reach.
Cookie and screenshot theft. When it swapped an address near wallet or payment wording, it also sent off the page URL, readable cookies and a screenshot.
iPhone exploits. On iPhones and iPads, it loaded the Coruna or DarkSword exploit kits depending on the iOS version.
The attacker kept working through the day, rebuilding the payload 26 times. One loader variant hid its URL in base64, and Smartsheet’s snippet was re-infected after being cleaned, a sign the attacker still held access.
Why crypto users should care
The address swapper is the part that hits crypto holders hardest. It validated checksums before swapping, so the attacker’s address looked legitimate. It also watched the clipboard, so copying an address from anywhere while an infected tab was open could paste the attacker’s instead.
Ledger’s spot on the list stands out. Its website is where many people start their self-custody journey, and its snippet carried the code until about 20:41 UTC. Hardware wallets show the destination address before signing, so comparing that screen against the intended address remains the strongest check. At the time of writing, Blockrora had not seen a public statement from Ledger.
On-chain, the haul looks small for an attack of this reach. Report URI counted about $7,040 flowing into attacker wallets by 19:25 UTC on 16 November, most of it in Bitcoin. StepSecurity put the figure nearer $6,600 and noted that some wallets had activity before the attack.
The attacker emptied those wallets early on 17 November, and one TRON address has been in use since March 2026. The larger unknown is the card and cookie data: Report URI says it cannot see how many cards or session cookies reached the attacker’s server.
What to do now
If you visited an affected site on 16 November:
Check any crypto transfer you made that day. If the recipient doesn’t match the address you meant to pay, it may have been swapped.
Update iPhones and iPads to iOS 18.7.3 or later, or iOS 26.3 or later.
Watch your card statements if you paid by card on an affected site.
From now on, verify the full address on your hardware wallet’s screen before signing, not just the first and last few characters.
If your site runs Optimizely Web:
Inspect every project’s Project JavaScript and experiment code for the domain 1688360.cc, base64 decoding calls, or any script you didn’t write.
Review which users, API tokens and integrations can write to your account, and rotate credentials.
Treat cards typed into your own forms on 16 November, and secrets in cookies not marked HttpOnly, as exposed.
Tighten your Content Security Policy. Of 159 affected organisations whose policies Report URI assessed, only 24 had one that blocked the payload.
The bigger picture
Optimjack is a supply-chain attack: none of the 178 brands had their own code breached. They loaded a script from a vendor they trusted, and that trust became the way in.
It may also be part of a wider run. Report URI tied the same actor to an earlier wave, starting 13 November, that pushed code through Kissmetrics, StorifyMe and Minute Media scripts. For crypto users the lesson is blunt: a familiar URL says nothing about the code running on the page, so the address on your signing screen is the only one to trust.
Sources: Report URI · StepSecurity · Optimizely status page · Cointelegraph
The Morning Brief
Start every day knowing what matters in tech
Six stories chosen by our editors, in your inbox at 06:00 UTC. Free.
Instant notifications in this browser when big news breaks. No email needed, and you can turn them off any time.
See more Blockrora in Google
Make us a preferred source and our stories show up more often in Top Stories.
Founder and Editor at Blockrora. A 20-year veteran of fintech, Web3 ecosystems, and software development, Warren writes on AI infrastructure, decentralised networks, and market reality checks. Trail walker and coffee purist.
More from Warren →